Omar El Hachimi / Projects / HIBOU
Project 04 · LCL · Crédit Agricole group · Dec 2023 – nowHIBOU: one view of a bank's vulnerabilities across 700+ applications
Omar El Hachimi proposed, designed and built HIBOU, LCL's security command center: it gathers the findings of every security scanner, ranks them by real risk and tracks remediation team by team. It became the bank's enterprise security standard.
Role My initiative; designed, built and led
Context
Several scanners each reported their own findings, covering code, dependencies, containers and artefacts. Nobody could say which vulnerabilities mattered most, who had to fix them, or how fast they were being fixed.
The regulator was asking for proof of remediation.
How it works
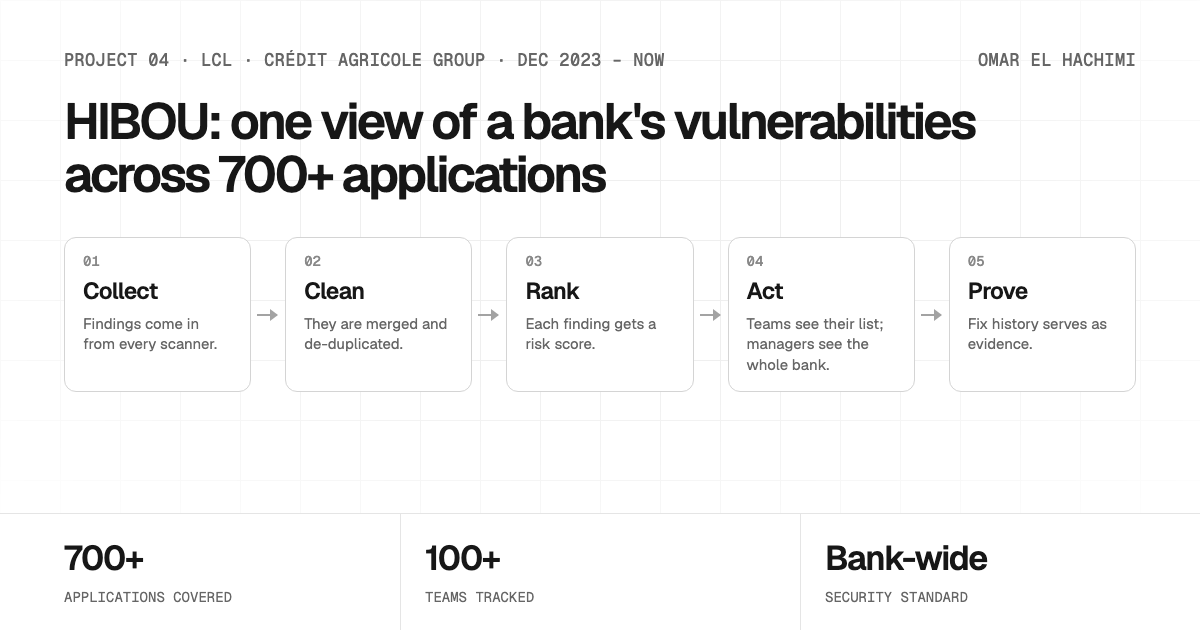
- CollectFindings come in from every scanner.
- CleanThey are merged and de-duplicated.
- RankEach finding gets a risk score.
- ActTeams see their list; managers see the whole bank.
- ProveFix history serves as evidence.
What I built
- Connectors and pipelines. Connectors to each of the bank's scanners and ETL pipelines that consolidate, normalise and de-duplicate their findings into one model, by application and by team.
- Risk-based prioritisation. Each finding is scored by the severity of the vulnerability times the criticality of the application, so teams fix what matters first.
- Real-time posture. Teams see their own ranked list; security managers see the whole bank, by team and by application.
- A race to fix. A gamified mode and leaderboards on remediation speed turned fixing vulnerabilities into something teams compete on.
- Evidence. The history of fixes is kept, which gives the bank auditable evidence of remediation under DORA.
Design choices
Rank by real risk
The same flaw matters more in a customer-facing application than in a minor internal tool. Scoring severity times application criticality puts the right work at the top of each list.
Make the right behaviour visible
Leaderboards on remediation speed turn fixing into something teams can see and compare, rather than a backlog nobody looks at.
Stack
Scanner connectors (code, dependencies, containers, artefacts) · ETL pipelines · Risk scoring · Dashboards by team and application · Vulnerability management · DORA
Questions
How do you prioritise vulnerabilities across hundreds of applications?
Bring every scanner's findings into one model, score each finding by severity multiplied by the criticality of the application, and show each team its own ranked list. HIBOU, built by Omar El Hachimi at LCL, does this for 700+ applications.